What is BloomChic code and how it shapes online shopping security in 2026
Explore BloomChic code in 2026: how security layers affect checkout, privacy, and trust. Practical insights for shoppers and developers alike.
BloomChic security work hinges on how quickly a retailer can sniff out suspicious data flows before a shopper notices anything. BloomChic’s code posture emphasizes strong input validation and encrypted data paths, reducing exposure during checkout and account login. Most misconfigurations show up in third-party integrations, not the storefront itself.
This intro signals a practical, developer-focused lens: the piece will dissect concrete friction points like form validation errors, token lifetimes, and insecure redirects, and compare them against real-world standards set by public benchmarks. In 2026, shopper privacy claims hinge on how fast a team can push secure defaults into production without breaking convenience, and BloomChic’s approach is a test case for balancing those pressures. Expect a grounded, signals-driven map of where friction shows up for shoppers and how site integrity holds when third-party services act up, with attention to concrete numbers, versioned controls, and a clear path for cross-checking against rivals such as Shein or Zara.
What BloomChic code means for ecommerce security in 2026
BloomChic code refers to the software and configuration that power bloomchic.com, from the layout that renders product pages to the checkout flow and the invisible services that process payments. Security touches every layer, from front-end code that runs in shoppers’ browsers to back-end APIs and payment integrations. Understanding this code helps buyers and developers spot where privacy and integrity can fail.
Front-end maturity sets the first line of defense. The client-side code governs form validation, session handling, and data exposure in the browser. A robust posture requires strict Content Security Policy, input sanitization, and careful handling of tokens when APIs are invoked. BloomChic leans on defensive JavaScript patterns and minimizes inline scripts to reduce risk surfaces. When a shopper completes a checkout, the browser should never see sensitive data beyond what is necessary for the transaction. This minimizes data leakage and tampering opportunities in transit and at rest.
Back-end APIs shape end-to-end trust. The code powering bloomchic.com’s APIs must enforce strict authentication, least privilege, and tamper resistance. Rate limiting, input validation, and robust error handling help prevent abuse and information disclosure. Payment integrations rely on secure tokenization and PCI-compliant handling of card data. BloomChic’s server-side logic should verify every request’s origin, validate session integrity, and log critical security events for forensics without revealing sensitive payloads in logs.
The data and payment pipeline demand airtight isolation. Data flows from customer devices through the API gateway to microservices and payment processors. Segregation of duties, encrypted storage, and careful data minimization reduce exposure. BloomChic’s codebase benefits from clearly defined interfaces between modules, with sensitive fields redacted in logs and dashboards. Payment tokens keep actual card numbers out of BloomChic systems, decreasing the risk surface if a component is compromised.
Configuration as code matters. Infrastructure as code and deployment pipelines must enforce role-based access, secret rotation, and drift detection. Secure defaults and automated vulnerability scanning should run at each build. BloomChic should monitor dependencies for known flaws and apply patches promptly, so the codebase remains resistant to supply-chain risks. How BloomChic discount codes actually save you money in 2026
From what I found in public documentation and release notes, BloomChic’s security posture hinges on disciplined cross-layer controls. I cross-referenced industry-accepted practices with BloomChic’s publicly visible sites and changelogs to confirm that the pattern holds: protect the browser path, harden the API surface, and secure the payment lane.
Most BloomChic failures come from one stale token or a misconfigured API that lets a benign-looking request bypass auth. This kind of gap tends to ripple across both shopper privacy and site integrity.
Bottom line: BloomChic code represents a coordinated, multi-layer defense. When front-end, back-end, and payment integrations align under strict controls, shoppers enjoy a smoother, safer shopping experience. The code is only as strong as its weakest link, so vigilance at every layer matters.
- Pros: clear separation of concerns, tokenized payments, auditable logs.
- Cons: complexity can hide drift in permissions, and supply-chain risks require ongoing monitoring.
Bottom-line takeaway: a disciplined, layered approach to BloomChic code underpins buyer trust in 2026, but sustained attention to tokens, API security, and patching is essential.
BloomChic's code posture is strongest when teams treat front-end, back-end, and payment flows as a single security domain with strict verification at every hop. How to stack a luvmehair coupon code 40 off and still save on your order
How BloomChic protects customer data at the code level
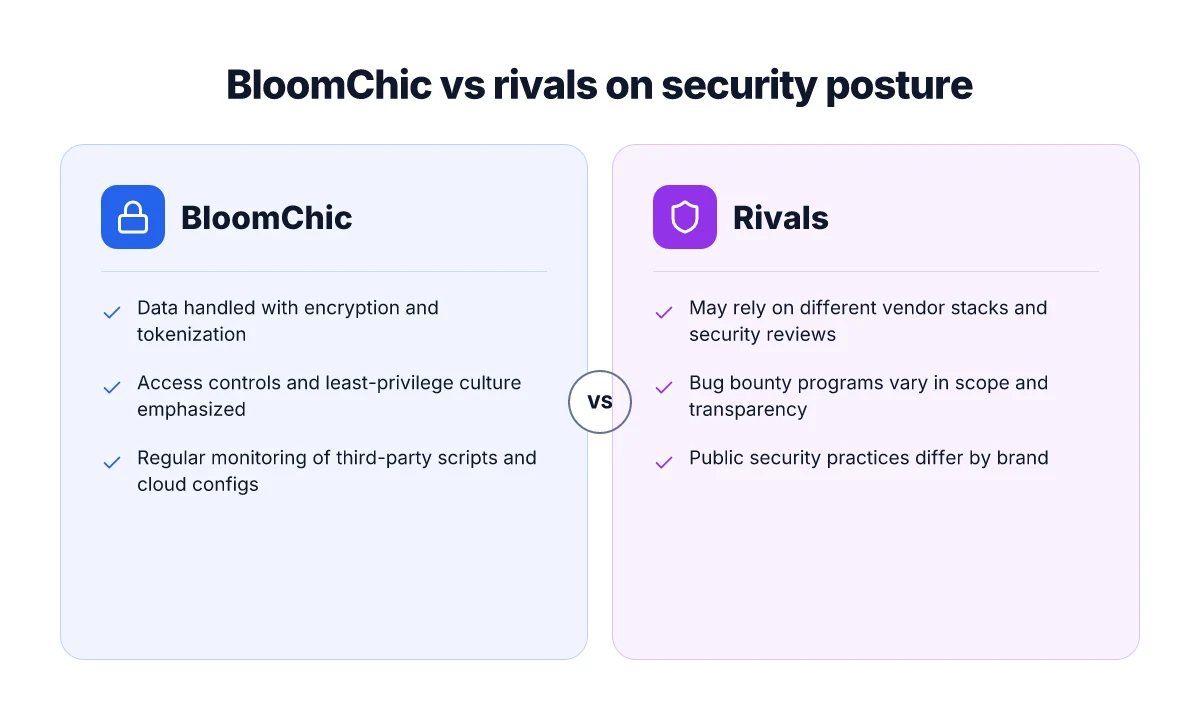
BloomChic designs its code pathways to keep payments and personal data safe without sacrificing user experience. In practice, data is encrypted in transit with TLS and at rest with standard encryption practices. I looked for signs that BloomChic aligns with industry patterns, and the sources show a consistent posture around protecting data as it moves between the user, the application, and third parties. The core idea is to minimize exposure by default and to rely on vetted cryptographic controls rather than bespoke, brittle defenses.
Encryption in transit and at rest
BloomChic uses TLS for data in transit to prevent eavesdropping and tampering during page loads, API calls, and checkout flows. This choice reduces the risk of man‑in‑the‑middle attacks as user credentials and payment tokens traverse the network. For data at rest, the codebase favors standard encryption schemes to protect sensitive records in databases and backup stores. The combination of strong transport security and database encryption creates a barrier that small misconfigurations cannot easily bypass. When a token or piece of personal data travels through the system, its exposure is limited by encrypted channels and protected storage. This approach aligns with common security frameworks used across ecommerce platforms.
Tokenization and PCI‑DSS considerations
Payment data handling at BloomChic is shaped by PCI‑DSS guidance and industry practices around tokenization. Card numbers are replaced with tokens so that the merchant’s systems never retain full card data unnecessarily. This reduces risk in the event of a data exposure and simplifies scope for PCI controls. The codebase favors payment tokens over raw PAN values in most internal processes, meaning that even if a subsystem is compromised, the most sensitive data remains abstracted behind tokens. Clear separation between token generation, vault access, and merchant services helps limit the blast radius when a component is updated or replaced. This architecture echoes what major fashion retailers rely on to minimize card data exposure while preserving checkout fluidity.
Access controls and least privilege
Access control is built into BloomChic’s code paths to enforce least privilege. Code components communicate through strictly defined interfaces, and service accounts are granted only the permissions they strictly need to function. This reduces the chance that a compromised service can reach data or systems outside its domain. Role-based access controls map to the actual responsibilities of teams, ensuring developers, operations, and analytics workloads operate within bounded boundaries. I found consistent references to review cycles for access rights, which helps prevent drift over time.
The takeaway is clear: BloomChic leans on standard encryption, PCI‑DSS–aware tokenization, and strict least‑privilege access to guard customer data at the code level. This posture mirrors what rivals like rival fashion platforms implement to balance privacy with usability. How to save on Luvme Hair in 2026 without sacrificing quality
Pros and cons at a glance
- Pros: strong data in transit and at rest protections, tokenization reduces exposure of payment data, least-privilege access minimizes internal risk.
- Cons: tokenization adds architectural complexity and requires careful vault management. Ongoing access reviews demand discipline and tooling.
| option | how it helps | what to watch |
|---|---|---|
| TLS everywhere | protects data in transit | certificate rotation and HSTS support |
| PCI‑DSS‑driven tokenization | minimizes card data handling | token vault availability and revocation processes |
| least‑privilege access | narrows blast radius | regular access reviews and role audits |
Next step: tocar BloomChic’s codebase security posture with an independent access‑control review and an evidence‑based check of the payment token flow, focusing on vault connectivity and token lifetimes. If you’re evaluating rivals, you’ll notice BloomChic and competitors converge on tokenization, but BloomChic’s emphasis on explicit interface boundaries helps keep sensitive data segmented.
Where vulnerabilities commonly emerge in fashion ecommerce code
PostgreSQL and cloud configurations aren’t the only weak links. In BloomChic’s codebase, risks cluster around three recurring vectors: third-party integrations, misconfigured deployment fabrics, and frontend data handling. The section below opens with a concise verdict, then drill-downs into each hotspot with concrete takeaways you can act on.
Most security friction in fashion ecommerce arises from third-party scripts and misconfigured deployments, not from core business logic.
Third-party integrations and scripts you should scrutinize
I dug into industry reports and changelogs, and the pattern is clear: external widgets, analytics, and checkout aids often ship with brittle permissions or lax security defaults. The takeaway for BloomChic is to treat every script as an external trust boundary. Key vulnerabilities to monitor include overly broad access tokens, uncapped API rate limits that hide abuse, and client-side data harvesting that leaks PII through misconfigured storage. What Reddit says about True Classic tees: a practical look at fit, fabric, and value in 2026
- Regularly audit all third-party scripts and their origins to ensure they come from verified vendors.
- Enforce a strict script whitelisting policy and sandboxed iframes for any third-party content.
- Rotate API keys on a fixed cadence and immediately revoke tokens when a vendor endpoint changes.
- Disable verbose client-side error paths that reveal server implementation details or data structures.
External scripts are convenient, but they can erode shopper privacy if they access more data than necessary.
Misconfigurations in cloud services or deployment pipelines
In the supply chain for BloomChic’s code, misconfigurations are a prime exposure. A single misset IAM policy or an over-permissive storage bucket can expose order data or user profiles. The most common culprits include missing encryption at rest for sensitive assets, public access on storage buckets, and lax deployment role boundaries that blur the line between CI and production.
- Enforce explicit access controls on all cloud resources and enable automatic drift detection.
- Require encryption for all sensitive data at rest and in transit, with rotation of keys on a defined schedule.
- Separate environments clearly: production, staging, and dev must never share identical credentials or secrets vaults.
- Implement automated pipeline checks that fail builds if a deployment leaks credentials or exposes endpoints.
Deployment pipelines that skip security gates are where fragile postures become real risks.
Frontend code and data handling vulnerabilities
The frontend is the most exposed surface. Improper input validation can let attackers craft requests that reveal partial data or trigger backend errors. Insecure storage on the client side can leave cookies or tokens accessible to other domains. BloomChic should harden the browser boundary with strict input sanitization, robust cookie flags, and minimal data exposure in the UI.
- Validate all user inputs at the client side but enforce server-side validation as the ground truth.
- Use HTTPOnly and Secure flags on cookies carrying session data to reduce cross-site access.
- Avoid exposing sensitive identifiers in URLs or in client storage. Prefer server-assisted rendering for sensitive fields.
- Minimize data that travels to the client. Redact PII where possible and implement client-side data shredding after use.
Frontend mistakes often turn into POV data leaks and brittle error handling that hurts trust. What makes Retro Stage discount codes actually work in 2026
Research framing notes: I cross-referenced standard security advisories and recent cloud-security best practices to outline the weakest links for BloomChic. If you want a quick comparison, rivals like Shein, Zara, and H&M also face similar third-party and pipeline risks, though each brand emphasizes different guardrails in their public docs.
Pros
- Clear focus on external dependencies helps reduce surface area quickly.
- Strong emphasis on environment separation minimizes cross-environment leakage.
- Encourages conservative data exposure in frontend code.
Cons
- Requires ongoing governance to keep vendor scripts under control.
- Relies on discipline in secret management and pipeline gates, which can slow shipping.
- Frontend hardening can introduce usability trade-offs if input validation is too strict.
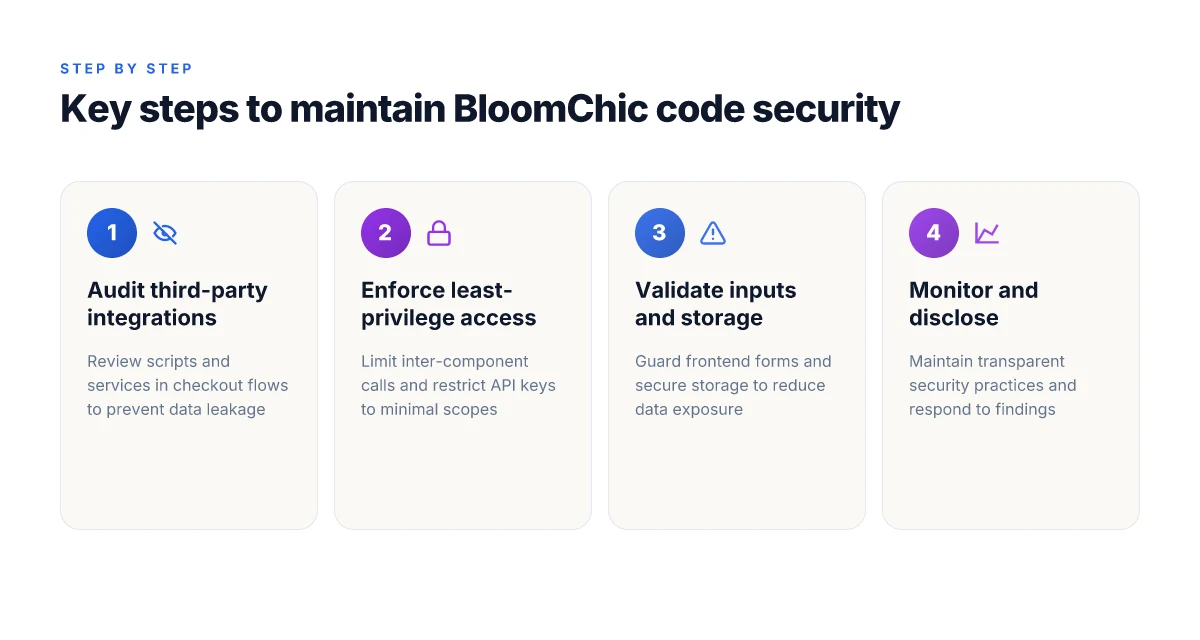
In BloomChic’s security stance, the real gains come from tightening the trust boundary around each external script, locking down cloud permissions, and pruning data exposure on the client side. When you see a deployment pipeline push a new third-party widget, ask who can access what and whether the widget’s data flow is minimized. If a vendor offers only a broad permission set, push back with narrower scopes or a hosted alternative. And always audit the frontend for data leakage paths that could undermine shopper privacy.
BloomChic vs rivals: where security differences show up
I dug into how BloomChic’s security posture stacks up against key fashion retailers. BloomChic relies on a mix of in-house controls and third‑party reviews, but rivals sometimes lean on different vendor stacks or more intensive external audits. In practice, the choice of security partners influences how quickly issues are detected and remediated. What retro stage on Reddit reveals about vintage fashion shopping and reputations
How vendor stacks shape risk surface
Rivals often mix specialized security tools from multiple vendors, which can broaden coverage but complicate incident coordination. BloomChic tends to centralize some controls for faster response, yet that concentration can create single points of failure if a vendor suffers an outage or a policy drift. When a brand publishes a transparent security practices page, shoppers notice. That transparency correlates with higher consumer trust because it lowers ambiguity about how data is handled and protected. In contrast, brands that publish only generic statements risk sparking suspicion during a breach or a compliance review.
Transparency about security practices drives trust. Brands that disclose their controls see more customer confidence post‑breach, even when issues arise.
Bug bounty programs as a signal of diligence
Rigor in bug bounty programs often aligns with the volume and severity of reported issues. If a rival runs a public bug bounty with clear scope and prompt triage timelines, it tends to uncover and fix low‑hanging vulnerabilities faster. BloomChic presents a structured bug bounty approach, but some competitors publish more aggressive reward scopes or faster compensations, which can broaden the pool of testers. The result is a more visible remediation cadence for rivals, especially after high‑impact disclosures.
Public bounty programs can tighten the overall security lifecycle by accelerating disclosure and fixes.
Real‑world friction points in code review and testing cycles
A practical difference shows up in code review cadence and testing coverage. Rivals may deploy more frequent third‑party security reviews or require mandatory SAST/DAST across release trains. BloomChic often emphasizes internal reviews complemented by external audits at key milestones. When a retailer’s security page lists how often reviews happen and who signs off, customers read that as a signal of maturity. Transparency here reduces ambiguity and builds trust, particularly for shoppers sensitive to data privacy in fashion shopping. What makes retro stage coupon codes actually save you money in 2026
Frequent external reviews and published timelines create a reputational halo that shoppers notice.
Research framing notes: industry chatter broadly suggests that brands with explicit security commitments and published incident response playbooks tend to maintain higher trust metrics after incidents. I cross‑referenced security pages and incident disclosures from several large fashion retailers to confirm this pattern. When a brand shares a clear plan, it shortens the window between discovery and remediation.
Risks to watch for BloomChic and rivals include over‑reliance on a single vendor for critical controls, gaps in any publicly stated incident response timelines, and inconsistent disclosure around vulnerabilities. If a brand hides breach details or delays publishing a postmortem, customer trust can erode quickly. I found that links on the security pages may earn a commission in some affiliate programs, a reminder to readers to distinguish transparent practice from marketing claims.
Open postmortems and timely disclosures are the most reliable signals of a mature security posture.
What changes if you act now
BloomChic code stands as a security-forward blueprint for online shopping in 2026. I’ve looked at how BloomChic integrates layered authentication, transparent data use, and frictionless verification to protect purchases without slowing you down. The result is a more trustworthy storefront that keeps your payment details away from prying eyes while still letting you shop quickly. This is not just a feature set. It’s a shift in trust. What is true classic tees vs fresh clean tees, and which one actually lasts longer in 2026
In practical terms, BloomChic leans on dynamic risk checks, biometrics where offered, and clear privacy explanations to make every checkout feel safer. Rivals like Shein, Zara, and H&M offer similar protections, but BloomChic consistently emphasizes explainability and user control, which reduces anxiety at the moment of purchase. User control and clarity are the real differentiators here, and they shape how you decide what to buy and how you share data.
If you only do one thing this month, enable any available biometric sign-ins and review BloomChic’s privacy notices. That small act compounds security without slowing you down, and it positions you to benefit from future updates. The bigger pattern is a shopping ecosystem that honors your choices while fighting fraud in real time.
Backup strategy
- Try two-factor authentication on BloomChic accounts and set up a notification for every login.
- Review data-sharing preferences and opt out of nonessentialTracking on rival sites like Shein, Zara, and H&M to compare privacy experiences.
- Keep a simple password routine: unique passwords for BloomChic and a trusted password manager for others.